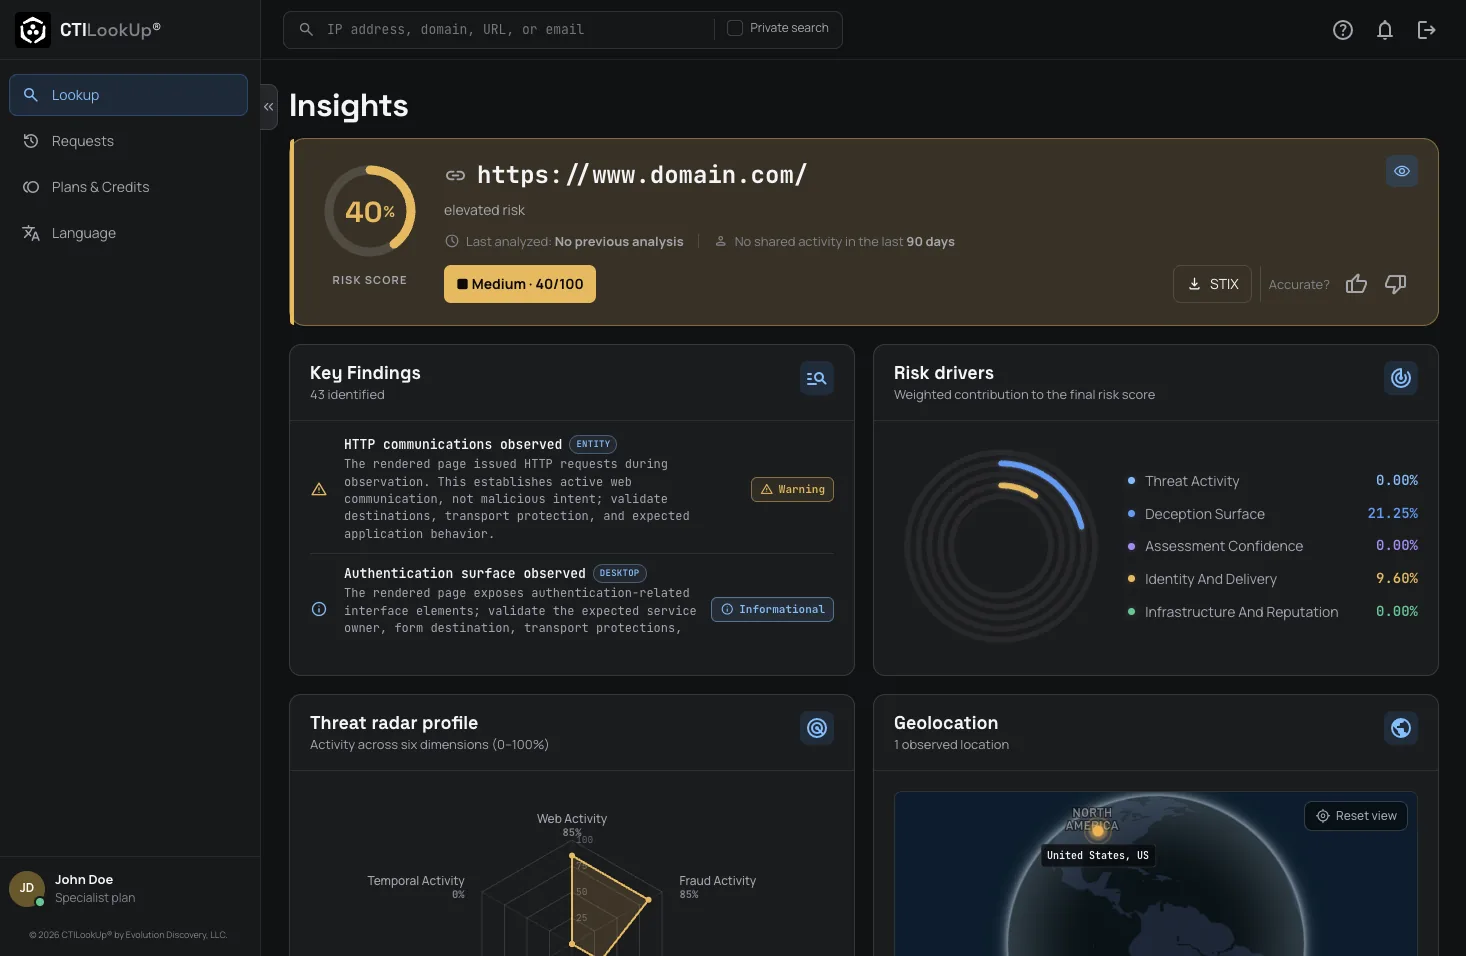
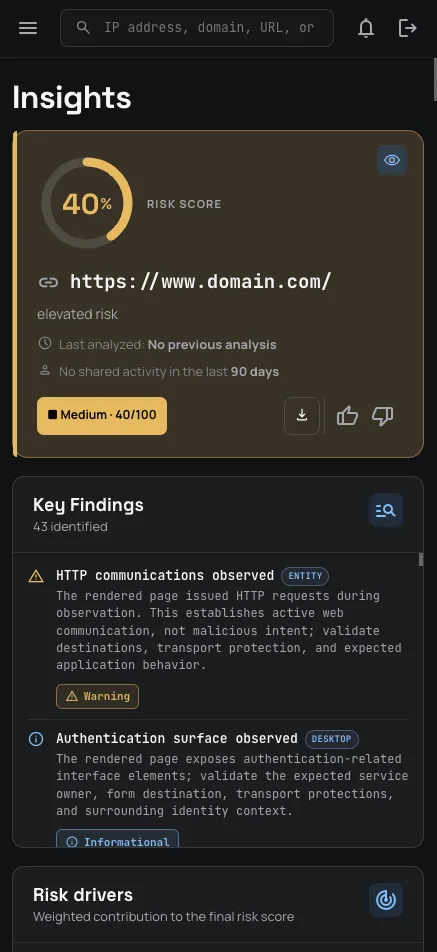
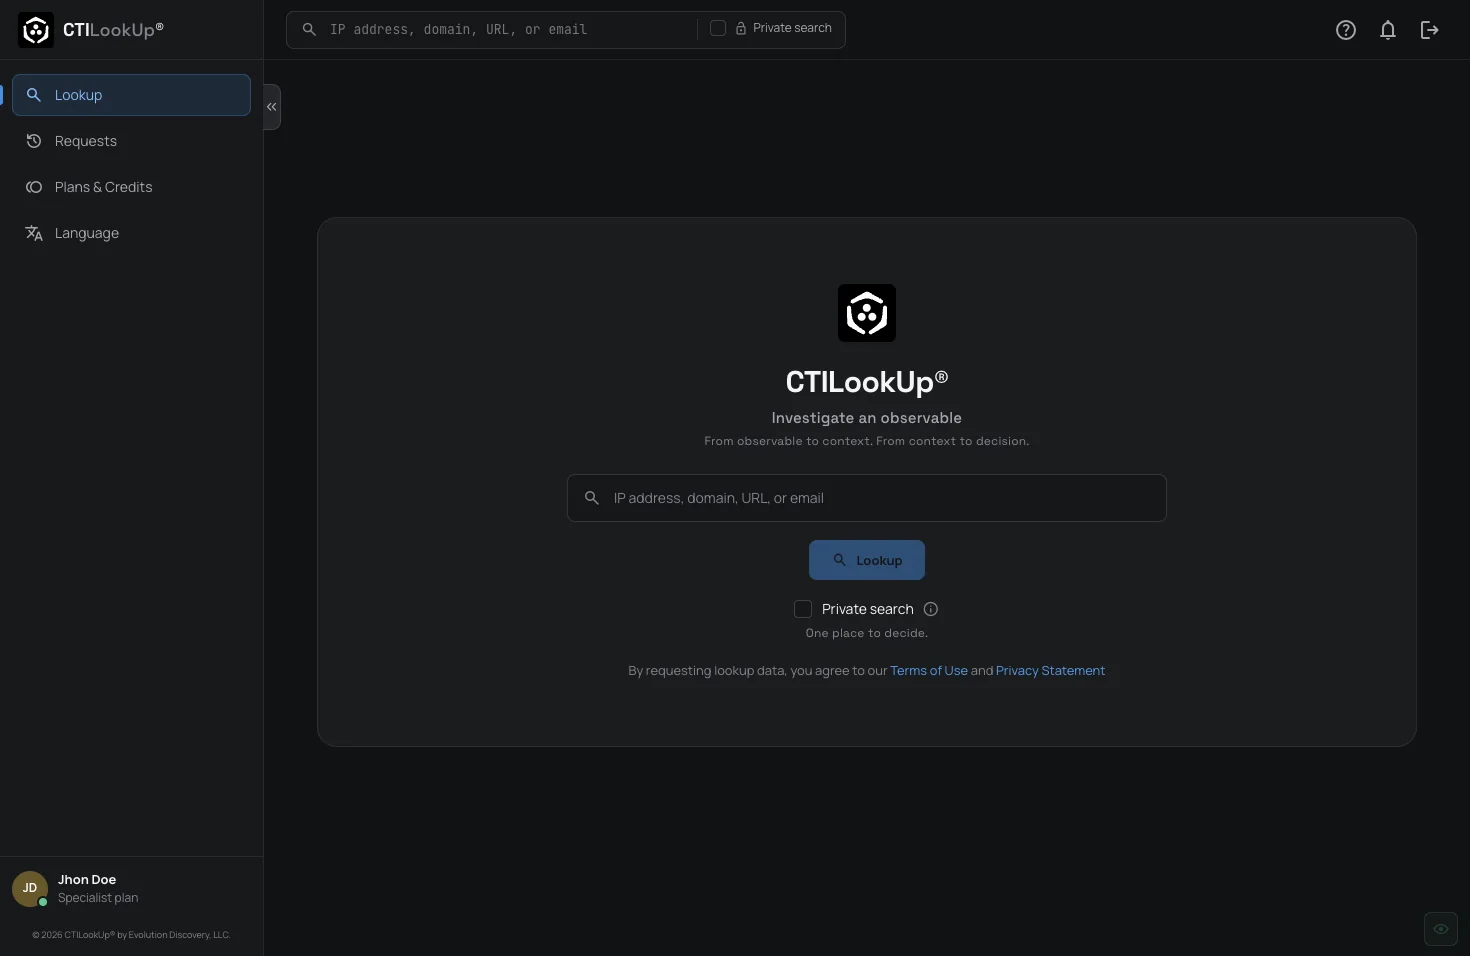
One investigation workspace, designed for desktop and mobile.
The operational gap
The problem isn’t more data. It’s making sense of it.
Analysts move across tools to validate sources, reputation, DNS, infrastructure, web evidence and temporal signals. The work is not collecting another result. It is separating evidence from noise and establishing context.
CTILookUp brings that workflow into one place.
One observable.Multiple signals.One place to decide.
Core intelligence loop
From observable to action.
A disciplined workflow for turning technical evidence into decision-ready context.
ObservableInvestigateCorrelateDecideAction
01
Investigate
Gather the evidence.
Enrich an observable with technical data, intelligence sources, security signals and relevant evidence.
02
Correlate
Connect the signals.
Identify relationships, anomalies, temporal context and meaningful patterns across multiple findings.
03
Decide
Understand what matters.
Transform correlated evidence into context that supports the analyst’s next operational decision.
Built for real investigation workflows
One workspace. From observable to context.
Investigate observables, correlate technical and intelligence signals, understand key findings and prioritize relevant risk without losing the investigation thread.
Unified observable investigation
Decision-oriented Key Findings
Risk score and weighted drivers
Threat radar and geolocation
Historical and temporal context
Structured STIX 2.1 output
Focused entryA direct path into the analyst workspace.Observable-first workflowBegin with an IP address, domain, URL or email.
Human in the loop
Intelligence that supports judgment — not replaces it.
CTILookUp does not automatically turn an isolated signal into a threat conclusion. It gathers evidence, correlates findings, provides technical and temporal context, and helps analysts understand what matters.
The analyst makes the decision.CTILookUp makes the decision better informed.
Use cases
Built for the people behind the decision.
For practitioners responsible for validating evidence and choosing the next operational action.
Relevant context, organized around the investigation.
Observable Intelligence
IP address
Domain
URL
Email
Context & Correlation
Technical enrichment
Infrastructure context
Security observations
Temporal context
Key Findings
Operational Intelligence
Risk assessment
Risk drivers
Threat context
Geolocation
Historical analysis
Outputs
STIX 2.1
Structured findings
Analyst-ready context
Pricing
Choose the depth of your workflow.
Plans and limits are shared with the CTILookUp application as the single product source.
IndividualInstitutional
Individual Cybersecurity professionals, independent researchers, consultants, and teams conducting personal or commercial threat intelligence investigations.
USD per user/license
Explore
User
$0/ user / month
Explore cyber threat intelligence analysis before moving into a professional workflow.
 CTI